Base hotel credential procurement on authorized roles and withdrawal procedures. Separate door access, system administration and mechanical backup before counting cards or selecting hardware.
Section 01
List authorized user groups
Define credentials from approved staff duties and the smallest access scope needed to perform them. Keep visitor permissions and mechanical backup under separate authorization and custody procedures. Purchase cards and supporting devices from that role record. Change the hardware or platform proposal when it cannot implement the required permission or withdrawal workflow.
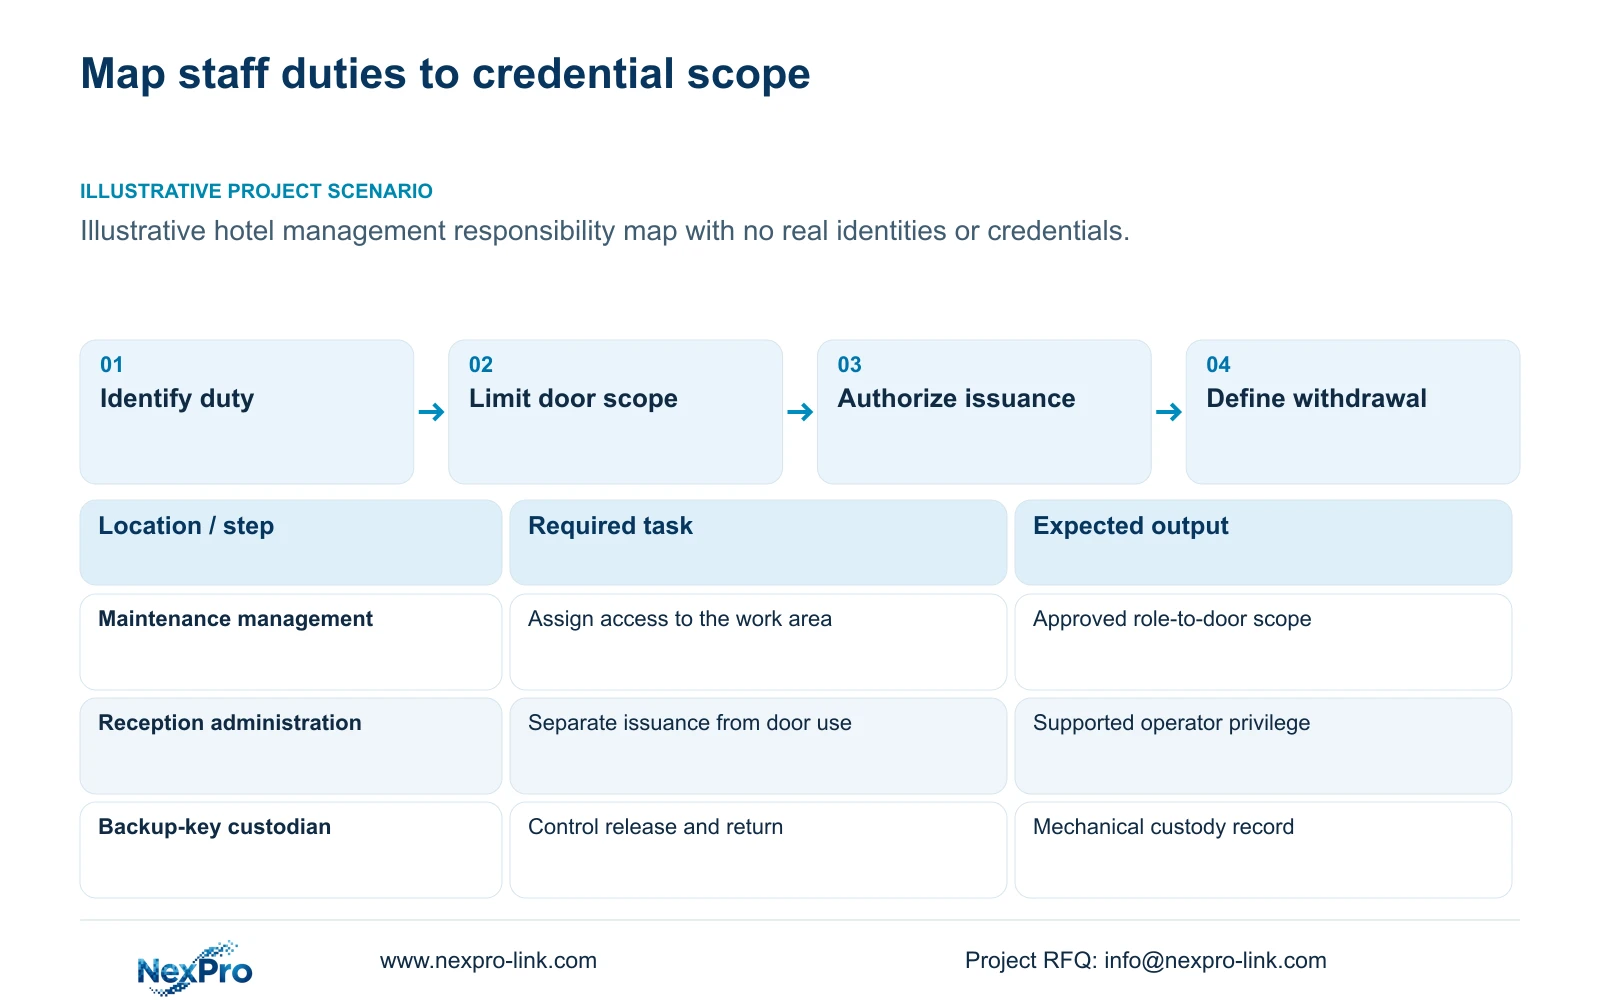
List the work performed by reception, housekeeping, maintenance, security and temporary service personnel where those groups apply to the hotel. A job title alone does not establish which doors a person needs to open. Record the permitted area and task, the approving role and the procedure used when the assignment ends or changes.
Distinguish door users from system operators. An employee may need to use a credential without permission to create one. An IT administrator may maintain equipment without a business need for general door access. The illustrative public-zone CCTV case has independent viewing roles and equipment counts; neither its room count nor its camera schedule determines master-card quantities.
| Required task | Given information | Decision still needed |
|---|---|---|
| Perform assigned maintenance | Work area and staff duty | Permitted doors and withdrawal process |
| Issue guest credentials | Reception responsibility | Supported issuance privilege and accountable operator |
| Use mechanical backup | Required fallback task | Authorized custodian, release and return procedure |
Section 02
Separate credential privileges
A credential's door privileges and its holder's software privileges need separate definitions. Opening an authorized door, issuing a replacement card and changing another user's access are different actions. Build a role-versus-task matrix that records required access first, then map it to controls supported by the selected system.
Keep account ownership, device binding and network access in separate records. Granting a person access to the management host does not establish permission to issue credentials. Likewise, a broad door credential should not become a default software-administration account. Where a requested restriction cannot be configured, disclose the gap before choosing the package.
Mechanical backup has its own control path. NX-HL-DQ is described in the hotel project source as an IC-card lock candidate with mechanical-key support. That does not establish a specific master-card hierarchy, revocation method or audit capability. Record who may hold and release the backup key, and keep safe operation with the responsible local specialist.
| Item | Combined privilege | Separated privilege | Effect on hotel task |
|---|---|---|---|
| Door credential | Broad access given by default | Access tied to assigned duty | Limits unnecessary door reach |
| Issuance account | Shared unrestricted operator | Supported task-specific role | Defines who can create or change access |
| Mechanical key | Informal shared custody | Authorized release and return | Defines responsibility for fallback use |
Section 03
Define issuance and revocation
Write the issuance procedure as an authorized request, supported configuration action and recorded handover. Identify who approves the privilege and who performs the encoding or account change. Keep unused credential stock separate from active credentials so possession of a blank card is not confused with an approved access assignment.
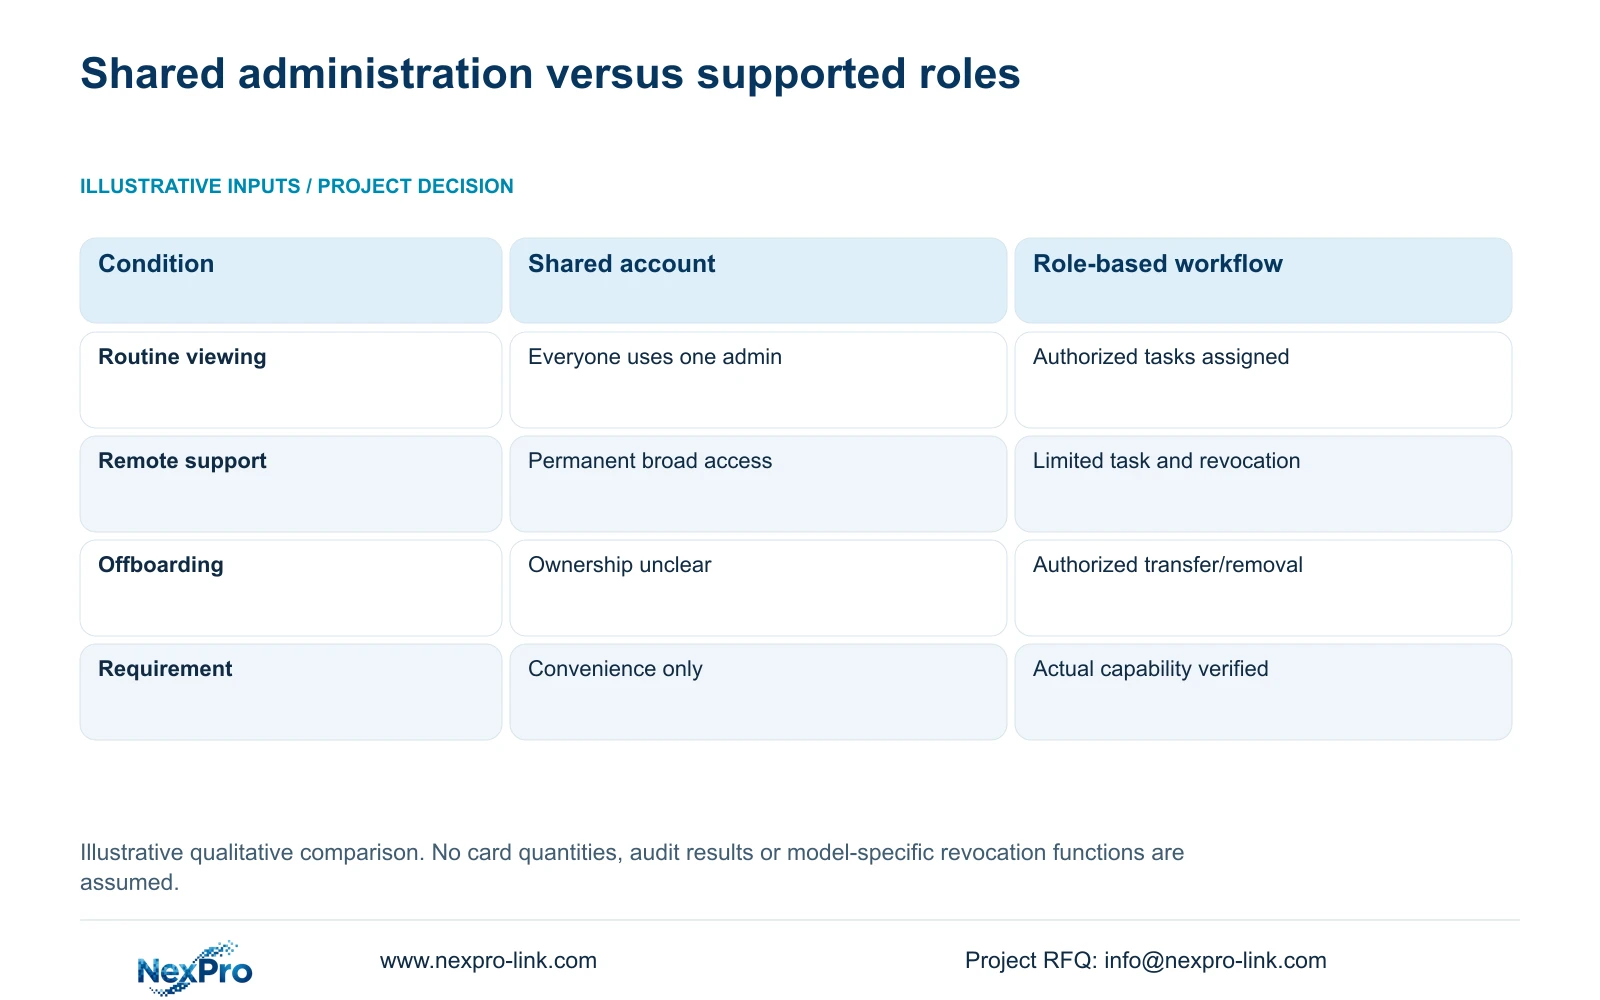
Define withdrawal before the hotel starts routine use. A lost credential, changed assignment or employee departure requires a supported method that reaches the relevant doors or systems. Physical return of a card and technical removal of its access are separate observations. Verify the intended method on the actual lock and software combination instead of assuming that deleting a record immediately updates every door.
Use the lifecycle checks below for the master-card scope, not a generic video-viewing account table. The original permissions illustration still explains why supported roles and removal matter; it does not establish a lock feature. Record who authorizes, encodes, receives and withdraws each credential, and keep mechanical-key custody separate. An unavailable revocation method is a procurement gap, not a pass.
| Stage | Record or observation required | Assigned responsibility |
|---|---|---|
| Authorize privileges | Approved doors, operating scope and recipient | Hotel access approver |
| Encode or configure | Actual credential/device/software and supported action | Authorized credential operator |
| Hand over | Recipient, assigned scope and custody record | Hotel credential custodian |
| Withdraw lost or departed access | Supported update route plus observed removal at relevant doors | Revocation owner; physical return alone is insufficient |
| Use mechanical backup | Approved release, return and custody process | Separate mechanical-key custodian |
Section 04
Compare audit and backup needs
Define the record the hotel needs to review after credential use or a permission change. Identify the authorized recipient, retrieval method and supported data scope. A requested audit function belongs in the requirements matrix until the selected system's capability is established. Avoid promising complete logging from an IC-card product description.
Separate electronic records from mechanical-key custody. A software report may describe supported electronic events without establishing how a mechanical key was handled. The fallback procedure therefore needs its own authorized release and return record. Decide how the hotel investigates an exception while limiting disclosure of guest information and privileged material.
Temporary technical support should use an approved task and a defined removal point. Initial inquiries should contain configuration identities and symptoms, not passwords or active master credentials. The comparison's limited-access recommendation applies to support as well as routine use. Hotel privacy and IT responsibilities must be settled for the actual location; this workflow is not a claim of universal legal compliance.
Section 05
Count cards and supporting devices
Build quantities from the approved role record and operating workflow. Separate guest credential stock, issued staff credentials and controlled replacement stock. The allocation basis should remain visible so a change in staff duties does not become an unexplained increase in cards. Do not apply a universal card-per-room multiplier to staff or master credentials.
Count encoders and management equipment from the locations that must perform supported issuance tasks. An extra station is worth evaluating when another authorized location needs that workflow or the agreed recovery arrangement requires it. Confirm the software, interface and service scope for the station; a second device alone does not establish operating continuity.
List compatible spares and local restoration responsibility separately. An unused credential or encoder may need review after the platform changes. The supplied current policy gives applicable main equipment a 24-month limited hardware baseline from receipt, subject to controlling terms. Credentials, accessories and any special order require their stated scope. Warranty does not replace a staffed issuance fallback or establish immediate local replacement.
Section 06
Prepare staff-change procedures
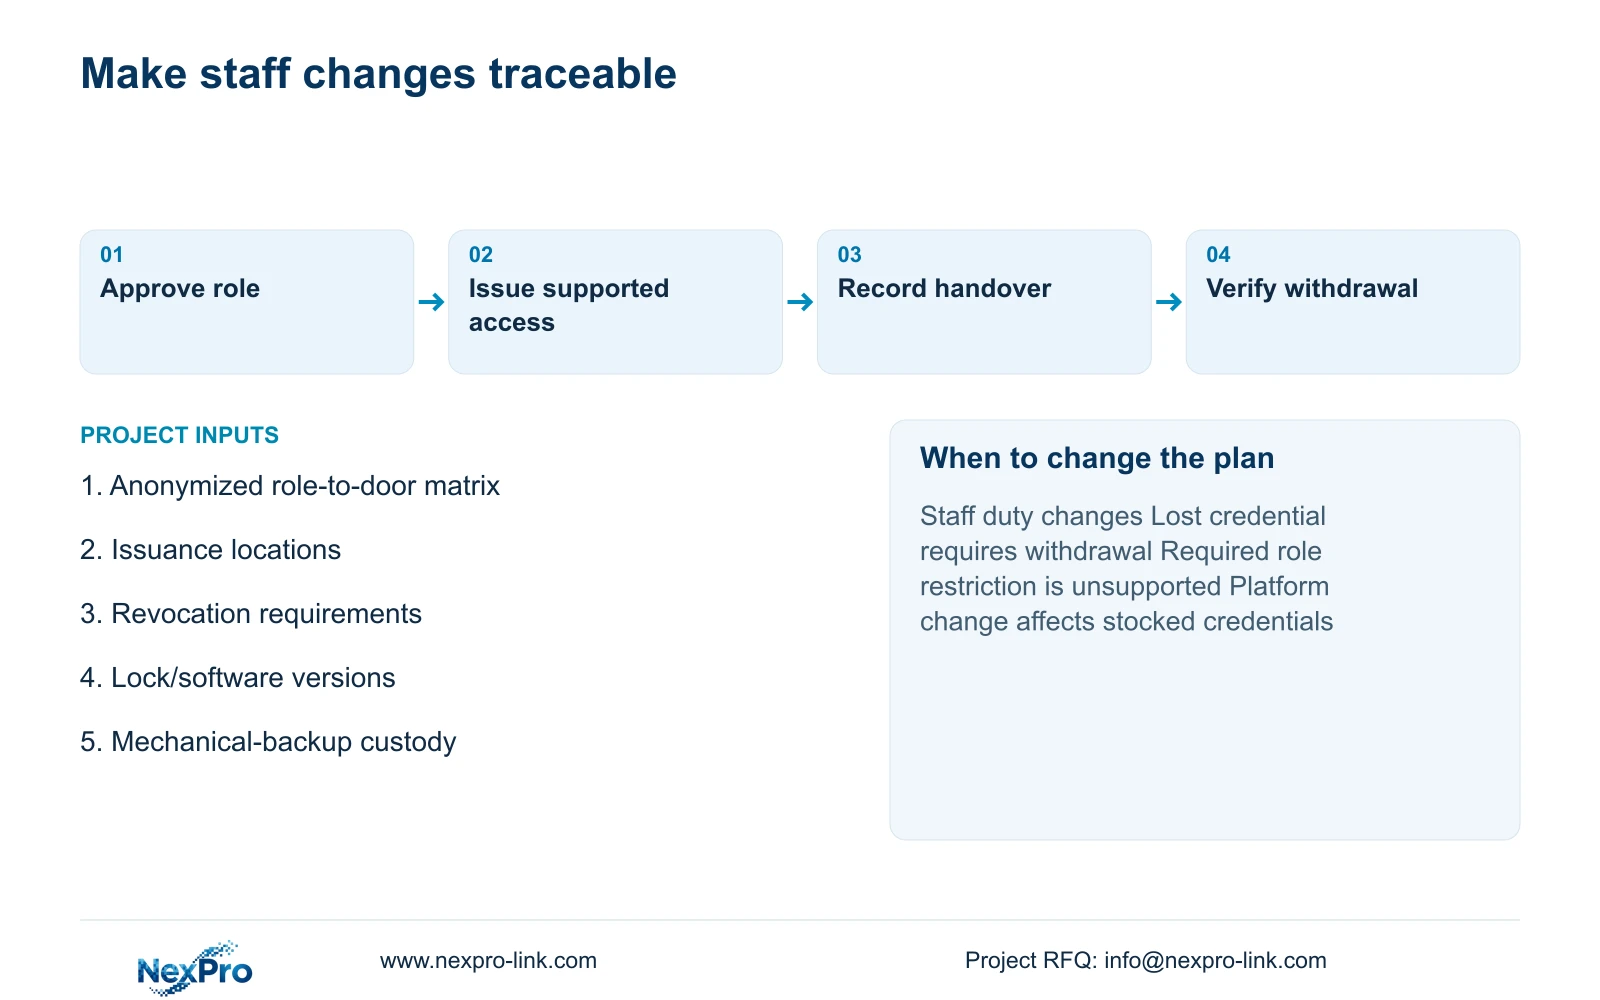
Treat an assignment change as a revision to the approved access record. Preserve the previous role and identify the doors, software privileges and physical items affected. Separate added credentials from changed privileges and any supporting-equipment change. Only the agreed configuration should become an order or an instruction to alter the operational system.
Handover should include issuing a permitted credential, withdrawing it through the supported method and returning controlled backup items. Record actual observations without claiming a demonstrated process covers every future configuration. Refresh the instructions when roles or equipment change, and identify who owns the hotel accounts after an installer or support provider leaves.
Send info@nexpro-link.com an anonymized role-versus-door matrix, the required issuance and revocation workflows, and selected lock or software versions. Identify mechanical-backup requirements and issuance locations. NexPro-Link can discuss a scoped equipment and BOQ response. Recommend the supported least-privilege arrangement when those duties can be implemented; revise the platform or configuration when a mandatory permission, audit or withdrawal task cannot be met.
Section 07
Buyer questions
Should every department receive a master card? No. Define the doors and tasks each department needs, then check the supported credential structure. Broad access should require an explicit operational reason and an accountable issuing authority.
Does collecting a departing employee's card complete offboarding? It completes the physical-return step. The hotel must also perform and verify the supported withdrawal of relevant door privileges, software accounts and any temporary support access.
Can a spare encoder guarantee uninterrupted issuance? No. Its supported configuration, software access and operator procedure still need confirmation. Evaluate a spare against the agreed restoration task, including who installs or activates it.
Engineering references
These sources support the general planning principles. Always use the selected product's current datasheet and applicable project standards for final design.