Treat the UPS management port as an asset that can execute power control, separating read-only monitoring from high-impact actions.
Section 01
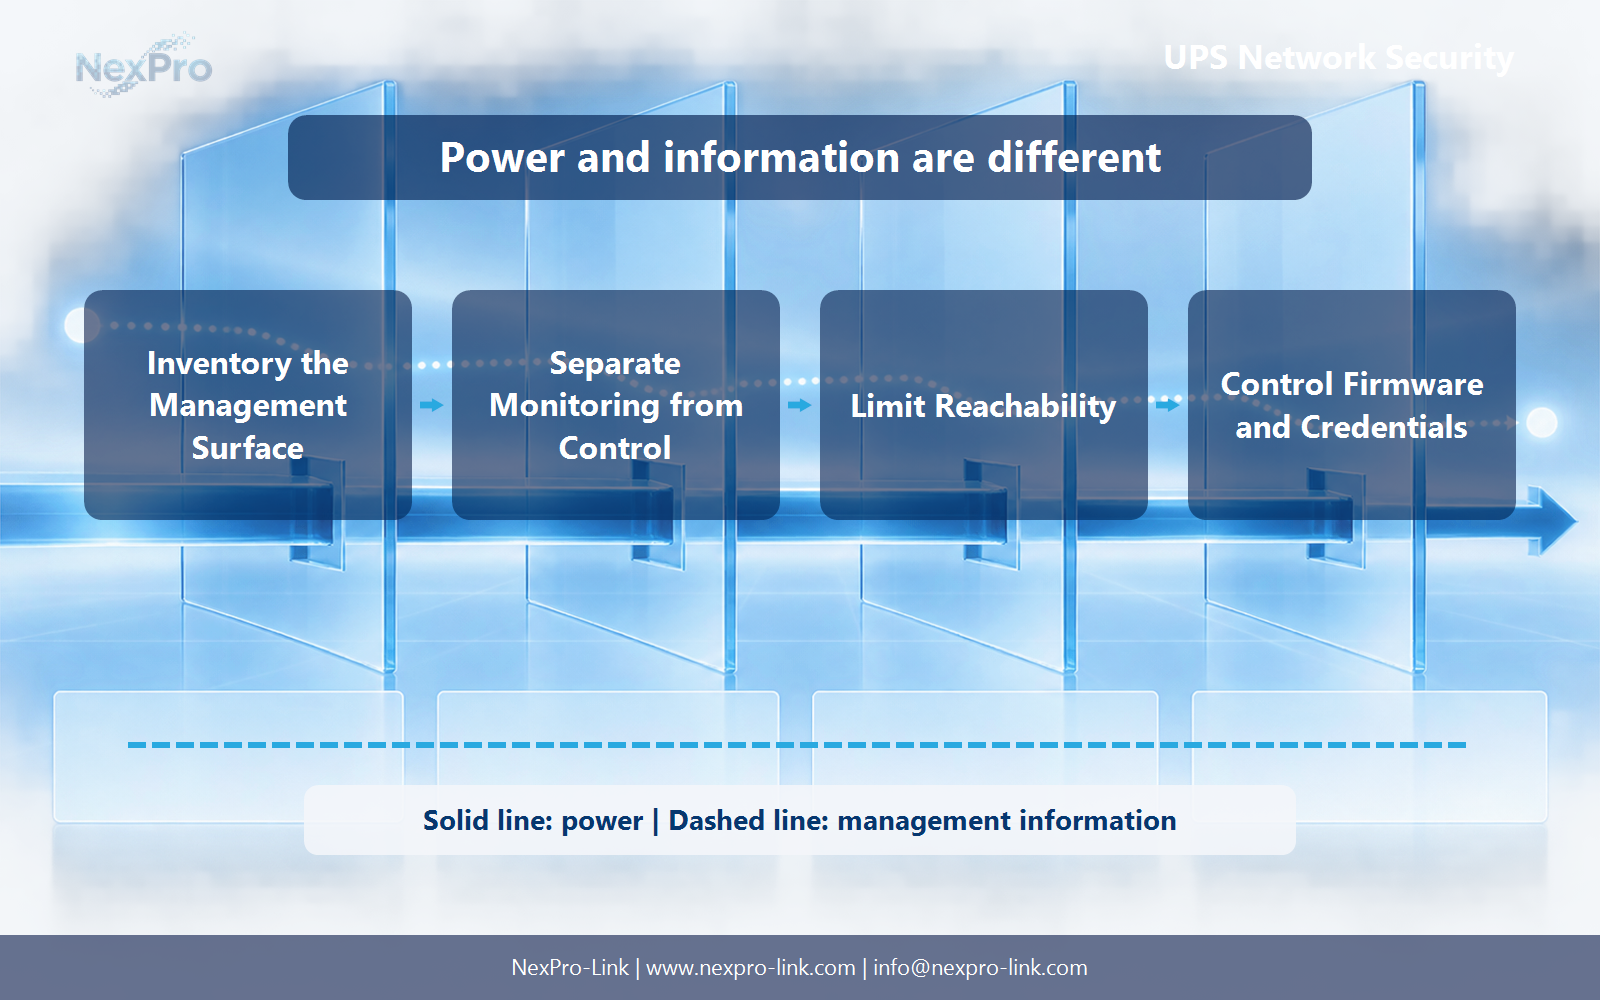
Inventory the full management surface
For IT/OT security engineers, the first project decision is this: Why should a UPS appear in the network asset register? A management card can expose configuration, alarms and sometimes power-control actions. Record the UPS and card separately with their firmware, address and owner. This establishes responsibility for a device that may otherwise be treated only as an electrical asset, without claiming that every networked UPS has the same vulnerability. The practical output is asset record: UPS / card / firmware / address / owner, supported by management-card version, network diagram and authorized control roles.
The management card is only one access point. Web interfaces, SNMP, command-line services, cloud connectors, USB links, serial ports, dry contacts and shutdown agents can all affect monitoring or control. Record which interfaces exist, which are enabled and who owns them.
Include the supporting switch, time source, name resolution and notification service. An interface that appears isolated may still depend on shared infrastructure. The inventory should show both the direct control path and the services required to keep it usable.
| Interface | Required action | Owner |
|---|---|---|
| Web or command interface | Restrict, encrypt and log | Infrastructure |
| SNMP | Use the required version and scoped access | Monitoring |
| Shutdown agent | Authenticate and test locally | Server team |
| Physical contacts | Document signal meaning and fallback | Facilities |
Section 02
Separate monitoring from control privileges
Reading input voltage or battery state is different from changing output groups, initiating a shutdown or altering network settings. Assign read-only monitoring wherever possible and reserve control functions for a smaller administrative path.
Service accounts should have one purpose and a named owner. Avoid shared default credentials, and place credential rotation inside the maintenance plan. If a shutdown agent needs control rights, document only the permissions required for that function.
- Give dashboards read-only access.
- Use separate administrator and automation identities.
- Log configuration changes and control actions.
Section 03
Limit reachability to the required management path
Place UPS management interfaces on a controlled network segment and permit only the systems that need access. Avoid exposing the interface directly to the public internet. Remote administration should pass through the organization's approved access path and logging controls.
A firewall rule is useful only when the address plan, ports and ownership are maintained. Include the UPS card in asset inventory, vulnerability review and configuration backup. Network isolation should reduce attack surface without preventing the local shutdown sequence.
Section 04
Control firmware while preserving outage resilience
Record model, firmware version, configuration backup and the process for reviewing vendor updates. Firmware changes should be scheduled with rollback and power-risk planning because the management path itself may be unavailable during the work.
The wider business network may fail during the same event that starts the UPS timer. Keep essential shutdown communication local where the design allows, and test the behavior with external services unavailable. Alerts are useful, but safe local action should not wait for a cloud connection.
Section 05
Buyer questions for UPS Network Security: Protect Management Cards and Shutdown Access
For IT/OT security engineers, these six checks separate UPS network management card security decisions from assumptions that belong to the wider project.
| Buyer question | Practical answer | Project output |
|---|---|---|
| Why should a UPS appear in the network asset register? | A management card can expose configuration, alarms and sometimes power-control actions. Record the UPS and card separately with their firmware, address and owner. This establishes responsibility for a device that may otherwise be treated only as an electrical asset, without claiming that every networked UPS has the same vulnerability. | Asset record: UPS / card / firmware / address / owner |
| Should everyone who reads UPS status be able to shut it down? | No. Visibility and disruptive control should have different permissions wherever the platform supports them. Define who may view, configure, acknowledge alarms or initiate power actions. Keep the proposal at the role-and-interface level until the actual management card is known, rather than promising features not supplied by that model. | Role matrix: view / acknowledge / configure / shutdown |
| Is placing a UPS in a VLAN sufficient security? | A VLAN is an architectural boundary, not a complete access policy. Define permitted management sources, routing and authentication, and avoid unnecessary public exposure. For a project-specific decision, record operator, management network, allowed service and UPS in the access path. This keeps the equipment inputs and intended service outcome aligned. | Access path: operator / management network / allowed service / UPS |
| How should UPS firmware updates be handled? | Track the UPS and card versions, review the supported update procedure and plan the effect on monitoring or control. Change defaults and protect administrative credentials through the organization's process. A staged maintenance plan is more useful than automatically installing every new release during production or claiming all updates are non-disruptive. | Change plan: versions / impact / window / rollback / owner |
| What happens when the management network fails during an outage? | The result depends on the shutdown integration and its local fallback behavior. Define how the system distinguishes a lost signal from a confirmed power event, and test in an approved environment. | Failure matrix: utility state / communication state / local action |
| What should buyers request from NexPro-Link? | Specify the necessary protocols, role separation, firmware information and integration targets along with the UPS load requirements. NexPro-Link can discuss available management options for the selected configuration. Do not label a whole product range enterprise-secure without defining the actual interface, deployment controls and supported features. | Management schedule: protocol / permission / logging / integration / scope |
Section 06
Turn the security policy into an equipment brief
The brief should state the allowed protocols, network segment, administrator roles, monitoring integration, local shutdown method and logging destination. It should also name the switch and host dependencies that need backup power.
During acceptance, test read-only monitoring, an authorized control action, credential recovery and a shutdown event with upstream network services disconnected. Keep the results with the configuration record rather than assuming that connectivity proves secure operation.
Engineering references
These sources support the general planning principles. Always use the selected product's current datasheet and applicable project standards for final design.